Black Friday Mega Sale 20% Off on CEH CPENT VAPT DA & DS

00d 00h 00m 00s
Grab the Deal
Professional Training

The CRISC certification by ISACA is the globally respected credential for professionals who manage enterprise IT risk. It validates your expertise in identifying, assessing, mitigating, and monitoring risks across modern digital environments. Our CRISC training at Securium Academy is designed with practical case studies, real-world frameworks, and exam-focused guidance to help you excel in governance, risk, and compliance (GRC) roles. Instructor-led CRISC training aligned with ISACA’s latest exam domains Understand enterprise risk, threat landscapes, and control design Master risk assessment, mitigation planning, and control monitoring Course Duration: 40–50 Hours Course Level: Intermediate to Advanced Course Delivery: Online
Start Your Research Journey

Request Program Details

Speak with our admissions team about CRISC.

Solve: 3 + 4 = ?

Program Highlights

Gain in-depth knowledge of IT risk management and control frameworks with CRISC training — learn how to identify, assess, mitigate, and monitor enterprise risks with real-world case studies and hands-on governance practices.

Instructor-led CRISC online training aligned with ISACA’s latest IT risk and control domains
Master risk identification, assessment, and evaluation techniques used in enterprise environments
Learn to design, implement, and monitor effective information system controls for risk mitigation
Learn from certified CRISC and GRC professionals with real-world governance and audit experience
Hands-on exercises in risk analysis, control mapping, compliance reviews, and continuous monitoring
Certification-focused preparation designed to help you confidently pass the CRISC exam on the first attempt

Why Choose CRISC?

Build Your Career in IT Risk & Controls with the Most Trusted CRISC Program

CRISC is a globally recognized credential focused on IT risk management and control. It empowers professionals to identify, assess, and mitigate enterprise IT risks while ensuring alignment with business goals and compliance requirements. Securium Academy’s CRISC training provides practical knowledge, case studies, and exam mastery to help you excel in governance, risk, and compliance (GRC) roles.

100% Exam-Oriented Training
Fully aligned with the latest ISACA CRISC domains and exam blueprint
40+ Hours Instructor-Led Sessions
Learn from certified CRISC trainers with real-world GRC experience
Hands-On Assignments & Cases
Risk identification, mitigation planning, control design, and governance
Complete Study Material Access
Slides, notes, mind maps, practice questions, and mock tests included
Recorded Session Access
Revisit and revise any session anytime without restrictions
Dedicated Mentor Support
Guidance for exam registration, planning, and doubt resolution
Enroll Now Course Curriculum
100%
Exam-Focused Training
40+
Training Hours

CRISC

Program Level Advanced

What You Will Learn

What You Will Learn
1️⃣ Governance (26%)
  • Enterprise risk governance principles and frameworks
  • Strategic alignment of IT risk with organizational goals
  • Accountability structures for risk ownership
  • Policies, standards, procedures & governance models
  • Legal, regulatory, and compliance requirements
  • Professional ethics & ISACA code of conduct
2️⃣ IT Risk Assessment (20%)
  • Identifying and analyzing enterprise IT risks
  • Evaluating risk scenarios and environment factors
  • Threats, vulnerabilities, and risk factor mapping
  • Business Impact Analysis (BIA) fundamentals
  • Understanding risk appetite, tolerance & thresholds
  • Risk scoring, prioritization & severity ranking
3️⃣ Risk Response & Reporting (32%)
  • Designing & selecting appropriate risk controls
  • Planning risk mitigation and response strategies
  • Implementation & integration of controls
  • Monitoring mechanisms for enterprise risk
  • Developing & analyzing Key Risk Indicators (KRIs)
  • Improving organizational risk posture
  • Reporting and communication with stakeholders
4️⃣ Information Technology & Security (22%)
  • Security control principles & governance practices
  • Infrastructure, network & application security
  • Identity and Access Management (IAM)
  • Cloud, virtualization & third-party risks
  • Data privacy, protection & security measures
  • Business continuity & disaster recovery planning
  • Risks of emerging technologies (AI, IoT, Blockchain)

Official CRISC Certification

Advance your expertise in enterprise risk management with ISACA CRISC, covering IT governance, risk identification, assessment, response, monitoring, and enterprise information security controls.
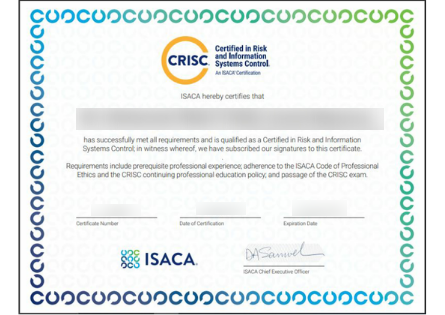
Official CRISC Certification

Become a Certified Risk & Information Systems Control Professional

CRISC (Certified in Risk and Information Systems Control) validates your ability to identify, assess, respond, and monitor enterprise IT risks. It is one of the most valued certifications for risk and governance professionals worldwide.

  • Master IT governance, policies, standards & regulatory frameworks
  • Learn enterprise-level IT risk identification & assessment techniques
  • Design and implement effective risk response and mitigation strategies
  • Develop expertise in monitoring risks with KRIs & reporting mechanisms
  • Understand information security, IAM, cloud, and emerging tech risks
Who Should Attend CRISC?

  • IT Risk Managers & Analysts
  • Information Security Managers
  • IT Governance & Compliance Professionals
  • IT Auditors & Assurance Specialists
  • Cybersecurity and GRC Professionals
  • Professionals managing enterprise risk & controls

Student Reviews

Exam was very nice.. It was an excellent experience.. I highly recommend everyone who is highly passionate in cyber security field should attend this exam.

Lajin C P

My overall experience is soo Good with Securium Academy. They have excellent trainers with Good teaching Skills. Especially My trainer so good in CYBER SECURITY knowledge with excellent practical knowledge. They also providing Coupons for the certifications

Malle Ganesh

Trusted Partners

Partnering with the world's leading universities and companies

Organisations across banking, government, fintech, consulting and energy trust Securium Academy to train their security teams.

  • Accenture
  • Big Basket
  • Central Bank of India
  • Central bank of iraq
  • Cihan
  • Credgenics
  • Deloitte
  • Ganani
  • HP
  • Indian Oil
  • Infosys
  • Iridium
  • K 24
  • KPMG
  • Kurdistan regianal goverment
  • malitec
  • Mobikwik
  • MOC
  • National Health
  • North Star
  • Pardiwala Security Pvt
  • Paymint
  • Phone Pe
  • plus wealth
  • RM
  • Sajag
  • Sarvatra
  • saudi
  • Saudi aramco
  • Savatra
  • TRAI
  • Udhmat

Recognition

Awards & Recognitions

Independent recognition for the quality of our training, labs and learner outcomes.

Hear it from our learners

Success Stories

Frequently Asked Questions

CRISC is ideal for professionals responsible for enterprise risk management, control monitoring, and IT governance, including:

  • IT Risk Managers
  • Cybersecurity & Governance Professionals
  • IT Audit & Compliance Specialists
  • Security Analysts & Consultants
  • Professionals planning to build a career in IT Risk & Control

CRISC focuses on enterprise risk and control lifecycle management, including:

  • Risk Identification
  • Risk Assessment
  • Risk Response & Mitigation
  • Risk & Control Monitoring and Reporting
  • Governance, Compliance, and Risk Frameworks
  • Business Continuity & Resilience Planning

CRISC has no mandatory training prerequisites. However, ISACA requires:

  • At least 3 years of cumulative work experience in IT risk and control
  • Experience across at least two CRISC domains

Training helps learners gain real-world understanding of risk and control processes.

Yes, CRISC is a globally recognized certification by ISACA. It is widely valued for validating risk management and control expertise in enterprises, financial institutions, and consulting firms worldwide.

CRISC training includes expert-led sessions, case studies, risk assessment exercises, and domain-based mock tests. Typical Duration: 40–45 Hours covering risk identification, assessment, control implementation, and reporting.

The CRISC exam evaluates your knowledge across risk lifecycle and control monitoring. Exam includes:

  • 150 multiple-choice questions
  • Covers all 4 CRISC domains
  • Duration: 4 hours

Passing Score: 450 / 800

CRISC-certified professionals earn between ₹10 LPA to ₹30 LPA based on experience, domain expertise, and organization. Risk managers and governance professionals with CRISC often secure high-paying leadership roles.

Securium Academy provides top-quality CRISC training with ISACA-aligned content, expert trainers, case studies, and domain-wise exam preparation.

×

Book Demo

×

Connect With Expert

Solve: 3 + 4 = ?
Enter the result of the math question above.
Connect With Expert
×

Apply Now

Solve: 3 + 4 = ?
Enter the result of the math question above.
×

Apply Now

Solve: 3 + 4 = ?
Enter the result of the math question above.